Another dimension · xsuri from our team
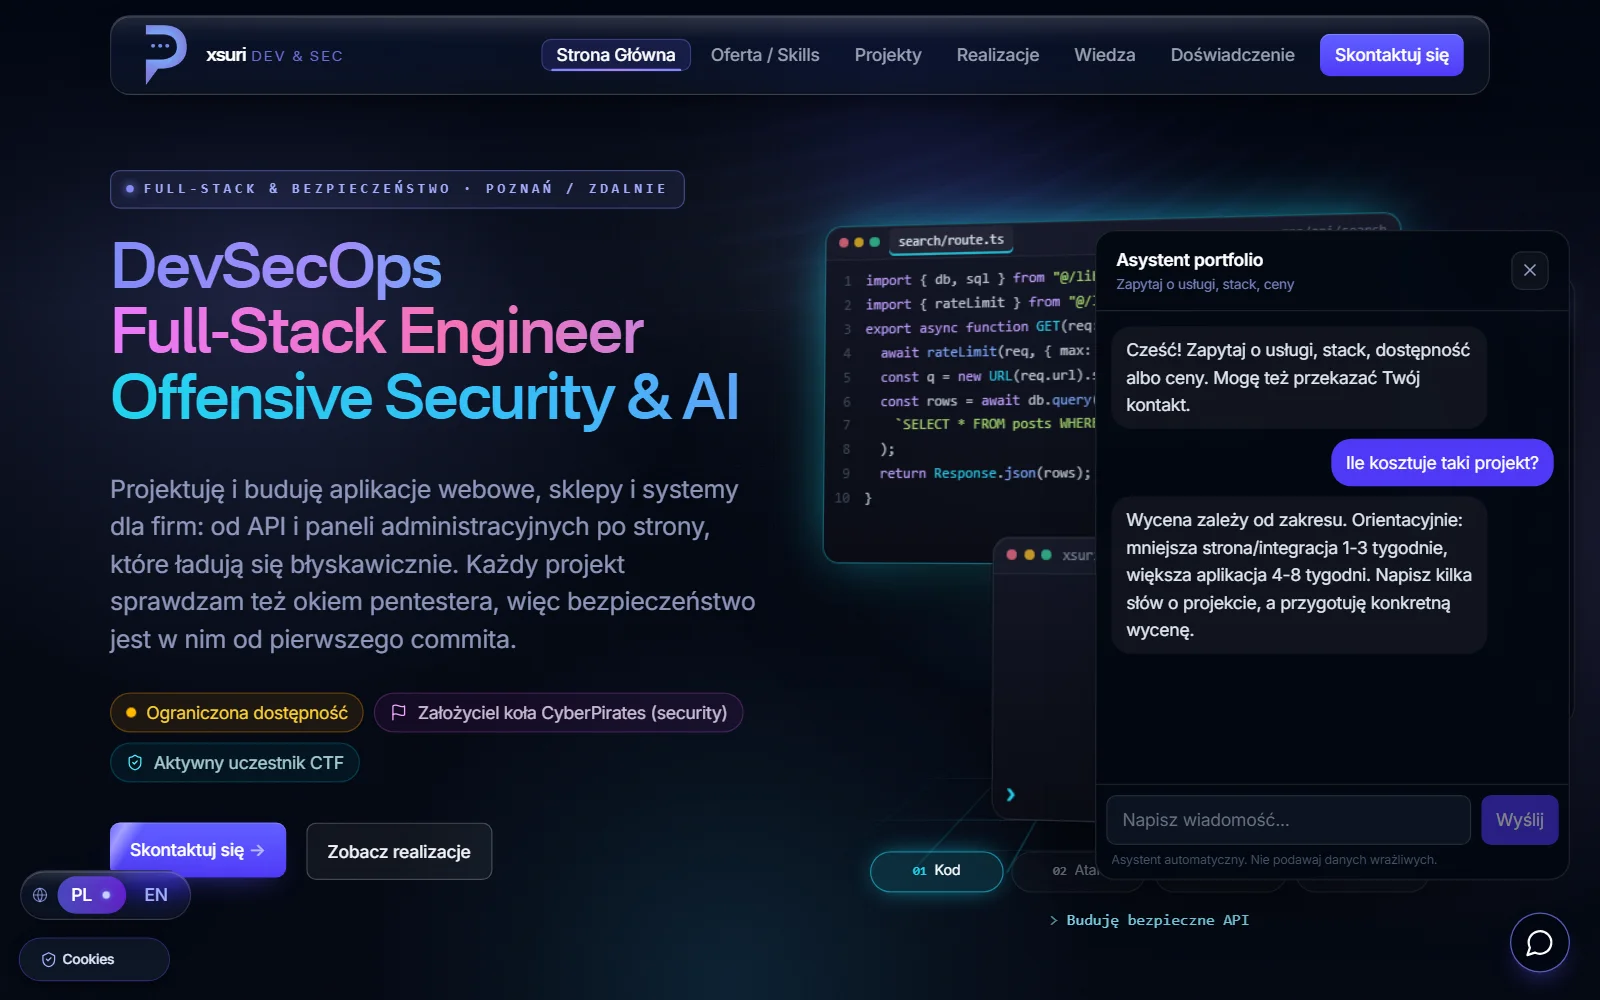
xsuri builds applications, then tries to break them. The site xsuri.cclabs.pl shows it from the first screen: code, attack, fix and ship. Further in, there is a terminal, hidden flags and a custom panel.
This scene runs live in your browser
A tour of the site
Eight things worth finding there
Keep scrolling and recordings of the site and panel play alongside. You can enlarge every shot. The leads and people in the panel are made up, there are no real enquiries. We won't give away the flags: those you have to find yourself. The recordings show the Polish version of the site, which also comes in English; the panel is in Polish only.
01Thread
The site changes color as you read
A glowing thread runs through the whole site, and the background shifts to the color of the section you are reading. Animations sleep when nobody can see them, and anyone who turned off motion in their system gets a calm version.
02Terminal
A terminal with something to find
Below the projects sits the line hack --start, and behind it a sandbox with its own file system, command history and a fictional lab server. It all happens in the browser and no real connection ever leaves it. Our recording stops before the flag: from there, you are on your own.
03Flags
Eleven flags hidden around the site
Type sudo on the site and a second console opens. Waiting inside are 11 flags hidden in places a pentester checks by reflex, a profile with a rank and a "find the vulnerability" quiz. The full set unlocks a mini-game and a certificate to download. The site compares submitted flags with SHA-256 hashes, so the code holds no list of ready answers.
04Work
A portfolio that keeps names private
You can narrow the work down to stores or applications, and the filter stays in the address, so a specific view can be sent to someone. Further down there are 25 website concepts for different industries. Without the company’s consent a card shows only the industry, and the name never even reaches the page code.
05Experience
Every certificate can be checked
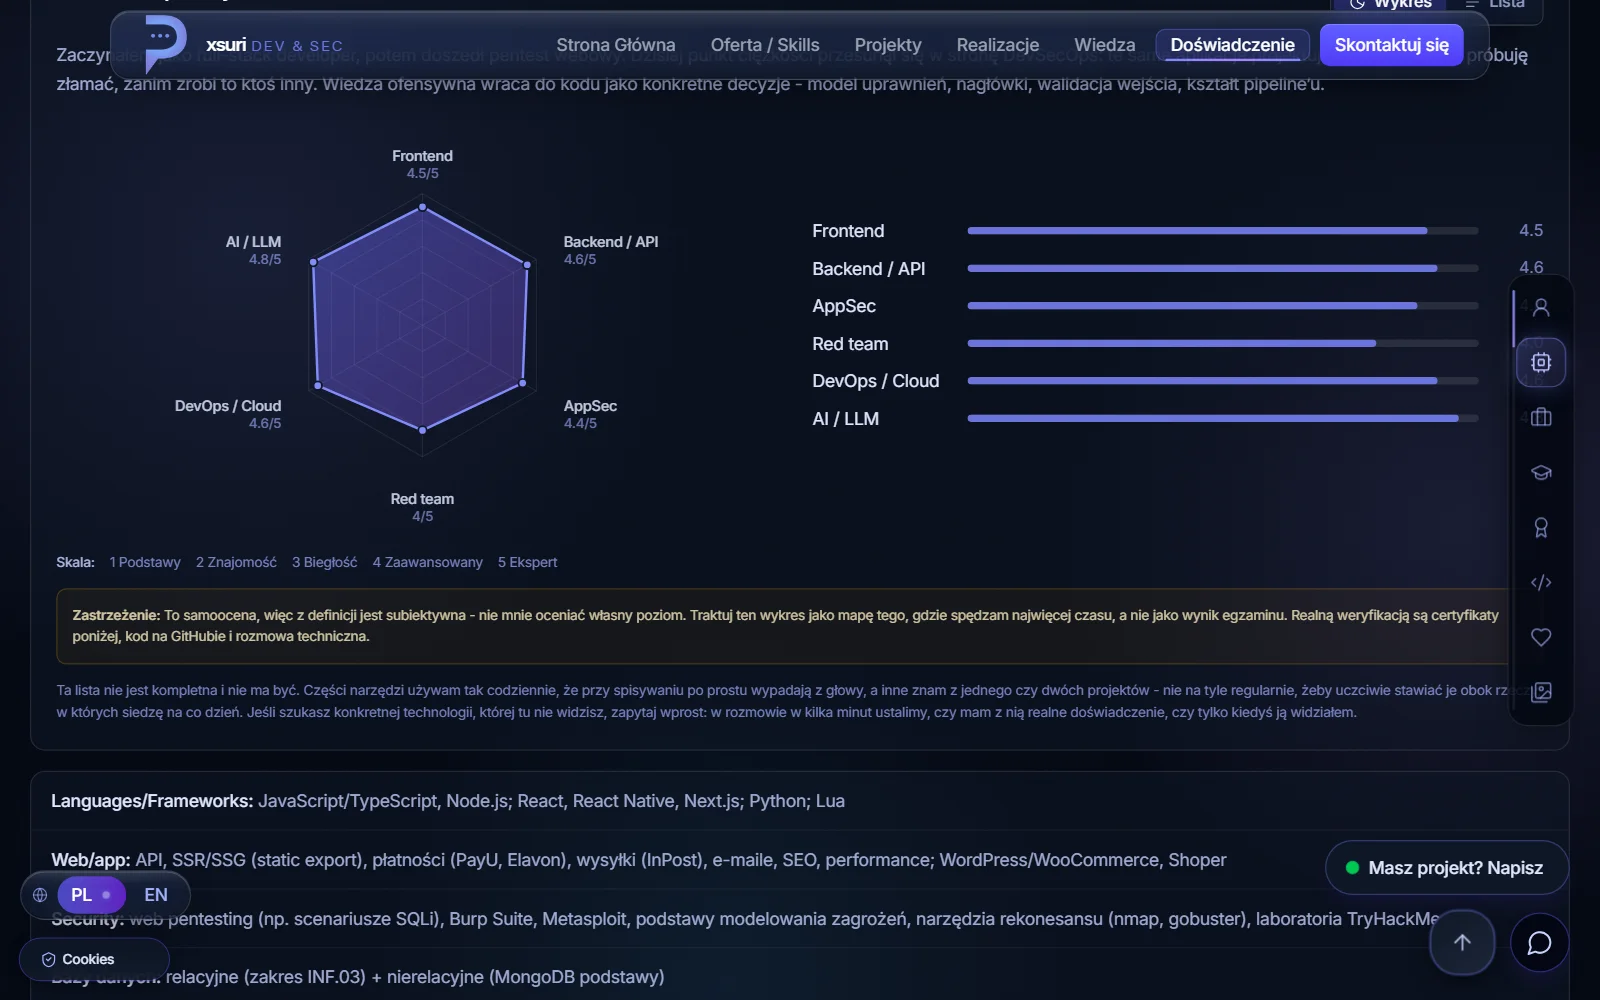
A career timeline, a skills radar and certificates linked to their issuers. The radar is a self-assessment and the site says so plainly; the proof is the certificates, the code and a technical conversation. The TryHackMe profile and badges sync on their own.
06Panel
A whole panel behind the login
Every enquiry from the form becomes a lead with a status, notes and an urgency rating, and spam goes straight to a separate list. Next to that are a dashboard of the working week, visit analytics and editing for all the site content. The leads in the recording are made up.
07Knowledge base
A custom editor for security write-ups
The application security knowledge base has an editor with "vulnerable code" and "fix" blocks, OWASP and CVSS classification, a 1:1 preview and publishing at a scheduled time. The first posts are still drafts, and one of them is in the recording.
08Under the hood
The same things he checks elsewhere
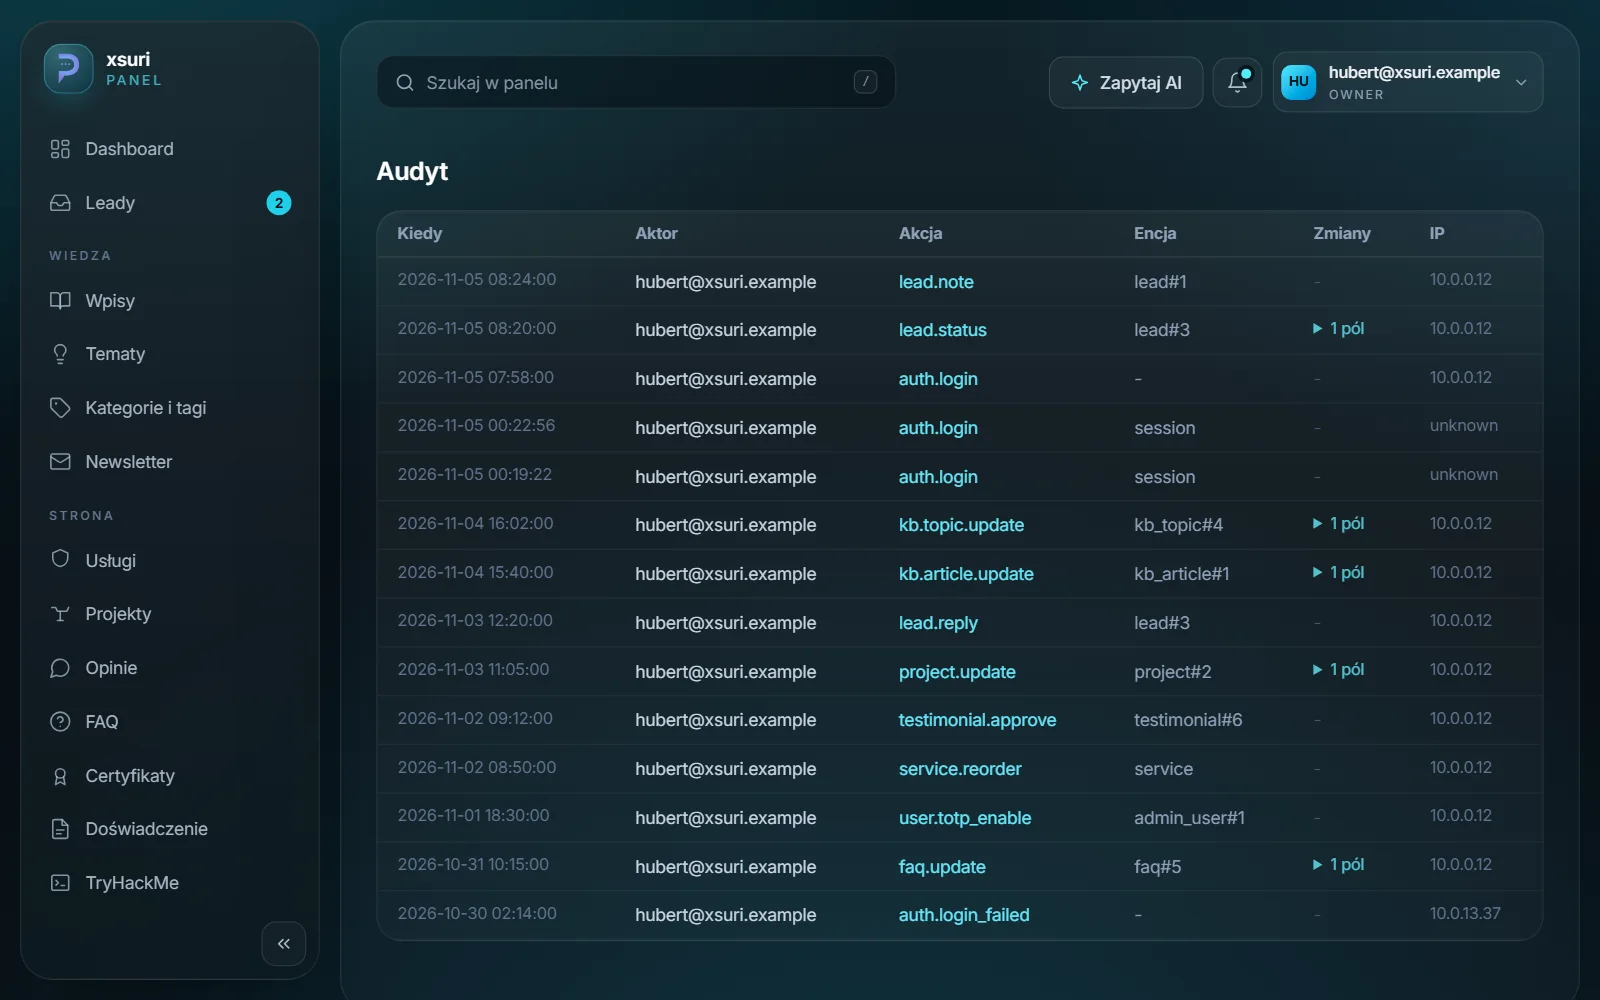
Passwords in argon2id, sessions revoked on the server, TOTP codes, roles and an audit of panel changes. The form has rate limits, a honeypot and a time trap, and on top come security headers, CSP reports and a security.txt file. The shot shows the change log with test data.
- Next.js 15
- React 19
- TypeScript
- PostgreSQL
- Drizzle
- three.js
Plus
The rest of the site
Small things that are easy to miss the first time round.
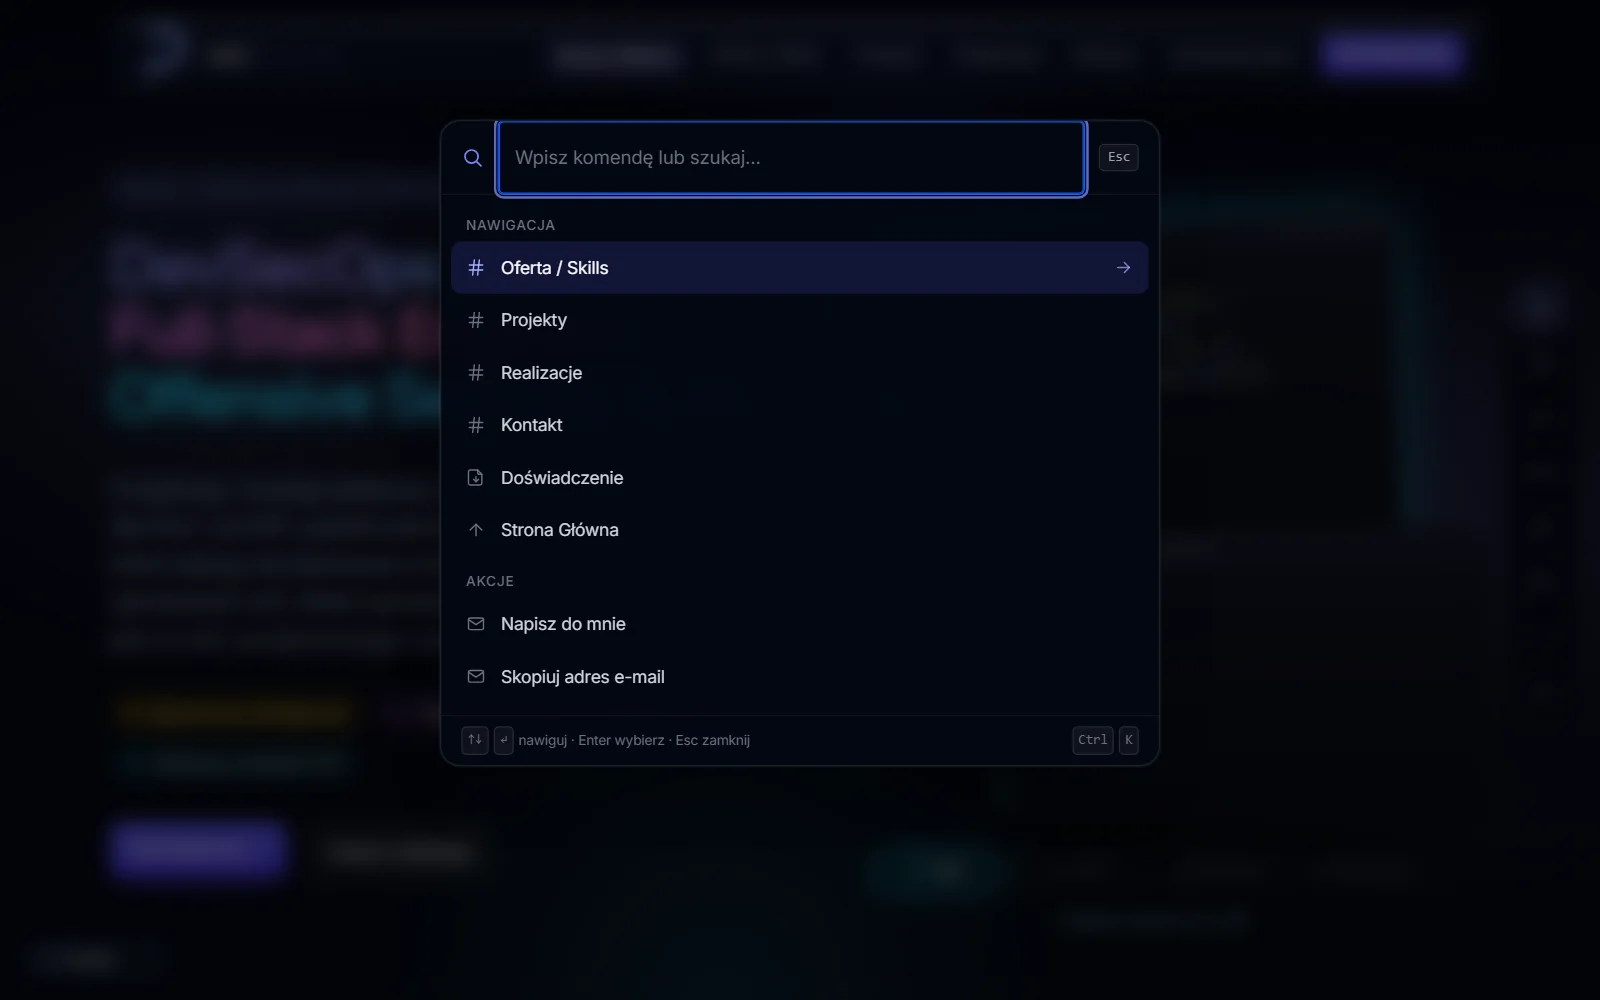
- Two languagesPolish and English, each with its own addresses and its own data for search engines.
- Analytics after consentIts own statistics and visit hashes that cannot identify anyone. Without consent nothing is sent.
- Newsletter with confirmationSigning up takes a click in the email, leaving takes one click, and there are no reader accounts.
- Works like an appIt can be added to a phone home screen, and when the connection drops it shows its own screen.
- Tests before deploymentLint, unit tests, Playwright scenarios and a full build on every change.
- Data with an expiry dateExpired enquiries and sessions disappear from the database on their own.
- Alerts and reportsThe server sends its own traffic and lead reports, and raises an alert on a sudden traffic spike.
- Full content without JSThe site renders on the server, so search engines and AI models see all the content, and llms.txt gives them the facts.
For your company
Someone will test your application eventually. Better if it's one of us.
xsuri runs OWASP-based web pentests and security audits for us: a report prioritised by real risk, help with the fixes and a retest. Testing starts only after written consent on the scope.